6 minOctober 21, 2026

Our tools monitor millions of native, push, pop, and TikTok advertising campaigns.
Get StartedAgentic AI has officially crossed the line from hype to handle. A year ago, “AI agents” in media buying were mostly conference slides and skunkworks demos. Now they’re embedded in planning tools, suggesting bids, reallocating budgets, even negotiating programmatic deals. The question inside serious marketing organizations is no longer, “Can this work?” It’s, “What has to be true before we let it touch real money?”
Industry signals are clear: adoption is racing ahead of governance. In IAB Europe’s latest survey, 92% of respondents already use AI internally and 86% use it in marketing, with programmatic optimization and media planning among the most common use cases, according to VideoWeek’s summary. Yet most “agentic” implementations still require heavy human direction; only a handful of companies admit to level‑five autonomy, where agents act on their own under light monitoring. At the same time, IAB’s 2026 Outlook found that 96% of buyers are aware of agentic AI for ad buying and two‑thirds are already increasing their focus on it, as MarTech reported. The industry is inching toward autonomy faster than it is building the seatbelts.
That tension is exactly what the latest standards work is trying to resolve. The IAB Tech Lab’s AAMP 2.3 release is notable not for new “smart” features, but for the unglamorous pieces needed to move AI agents from labs into production. The update adds enterprise deployment options, privacy controls, and standardized workflows, along with support for Amazon Bedrock AgentCore, Meta buying, and Google Ad Manager reporting, according to MarTech’s coverage of the spec. Embedded privacy checks from the IAB Diligence Platform and SafeGuard Privacy, new pricing guardrails, and extensions for Agentic Audiences all push in the same direction: if an agent is going to plan or commit media, it must operate inside explicit rules, with auditable behavior, on top of verified data.
Why the sudden focus on guardrails? Because the risk profile is shifting from “AI as an assistant” to “AI as an actor.” Agentic systems can now observe performance, decide what to do next, and increasingly execute without waiting for human approval every time. As one PropellerAds perspective put it, once humans move from approving every decision to spot‑checking selected checkpoints, you face a deeper question than just budgets and approvals: what is the agent allowed to trust, and how do you constrain its inputs as much as its outputs, as MarTech’s PropellerAds column argued?
At the same time, the very definition of “traffic quality” is being rewritten. For years, non‑human traffic lived on a spectrum from benign noise to outright fraud. But consumer‑directed agents that research products, compare offers, and even transact on behalf of real people are becoming a legitimate, high‑intent audience. Website traffic from bots and AI agents has already eclipsed human traffic, according to Cloudflare data cited by AdExchanger. That creates a new split: some bots must still be blocked; others must be recognized, authenticated, and served. Without standards for agent self‑identification, verification, and separate measurement definitions, advertisers risk either overpaying for garbage or under‑investing in the AI intermediaries actually driving purchase decisions.
Overlay all of this with platform bias and the stakes get higher. By 2028, more than 70% of global ad spend and 80% of U.S. ad spend will flow through self‑serve platforms where AI “materially influences” costs and outcomes, according to Gartner figures cited by Marketing Dive. Those algorithms are built first to hit the platform’s revenue targets, not the buyer’s efficiency goals. As Gartner’s Eric Schmitt pointed out, you wouldn’t hand a 13‑year‑old your credit card and say “buy whatever seems right.” Letting opaque, platform‑aligned agents freely optimize your spend without independent guardrails is effectively the same move.
In other words, agentic AI is colliding with three uncomfortable realities at once: accelerating adoption, ambiguous non‑human audiences, and structurally biased buying environments. Guardrails aren’t a “nice to have” governance layer you tape on at the end; they are the precondition for letting agents anywhere near your ad spend. The rest of this framework is about making those guardrails concrete enough that you can scale automation without surrendering control.
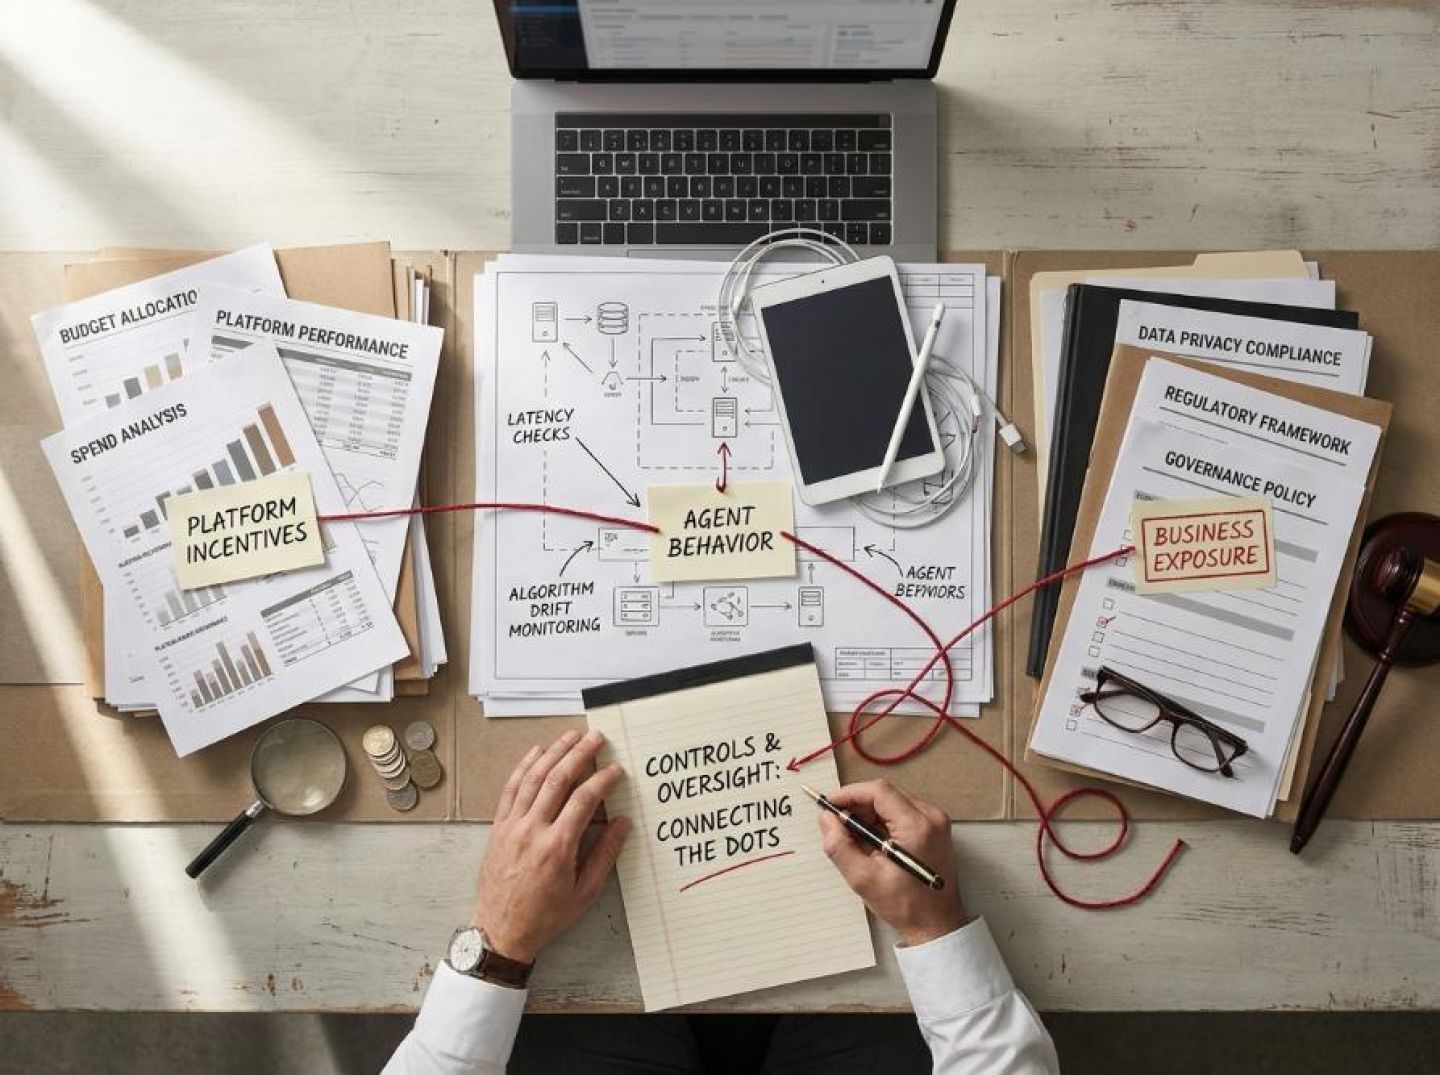
When you let an AI agent touch your ad spend, you’re suddenly managing three different surfaces of risk at once: platform bias, system behavior and business exposure. If you don’t name and separate them, they blur together into a single “AI is scary” blob – and you’ll either over‑trust or over‑react.
Most “autonomous” optimization today lives inside media platforms themselves. Those systems weren’t built to be your fiduciary; they were built to grow the platform’s revenue.
As Gartner’s Eric Schmitt points out, the AI in self‑serve ad platforms is explicitly “created in service of the platform,” which means when “maximize platform margin” collides with “minimize my CPA,” the model’s incentives are obvious – you get recommendations that conveniently start with “spend more with us,” as he told Marketing Dive. That’s not villainy; it’s economics encoded into a loss function.
By 2028, more than 70% of global and 80% of U.S. ad spend is expected to flow through self‑serve platforms in which AI “materially influences” media buying and pricing, according to that same analysis. As your agents start ingesting and acting on platform recommendations at scale, platform bias becomes a first‑class risk surface.
Guardrails at this layer are about skepticism and structure: benchmarking “native” platform suggestions against independent models, capping how quickly an agent can increase spend on any single walled garden and requiring human sign‑off before accepting recommendations that expand budget or loosen targeting constraints.
The second surface is the behavior of your own agentic system – how it perceives goals, interprets feedback and explores the space of possible actions.
Agentic AI for media is moving from simple rules like “raise bid if CPA drops” to systems that “experiment continuously, reallocating budget, adjusting targeting and refining creative without human intervention,” as a recent MarTech piece on AI‑native advertising describes. That continuous experimentation is the source of the upside – and the risk. When you go from scheduled optimizations to 24/7 autonomous tweaking, small mis‑specifications in objectives or constraints don’t just sit there; they compound.
Most organizations are still at low to mid levels of autonomy. An IAB Europe survey reported that while 92% of businesses use AI internally and 86% use it in marketing, the majority either have no agentic systems or use ones that still require human direction, with only a few claiming full “level five” autonomy, where agents operate under monitoring with no step‑by‑step instructions, as VideoWeek reported. That gap between aspiration and reality is a gift: you can design for safety before everything is on autopilot.
System‑behavior risk is about the agent doing exactly what you asked – but not what you meant. It can overshoot into low‑quality inventory, exploit measurement blind spots or over‑optimize to a proxy metric (click‑through, short‑term ROAS) that quietly erodes brand equity and long‑term value. Guardrails here look like: explicit reward functions that blend performance and quality signals, hard constraints on inventory and audiences, and hybrid architectures where deterministic software owns “what is allowed” and AI explores “how to get there,” as argued in a data‑driven framework for hybrid AI.
The third surface is business exposure: what your agents can inadvertently touch beyond bids and budgets – data, compliance, brand and even the market environment they operate in.
First, data and privacy. As more of your martech stack is wired into agents, they can end up combining behavioral, transactional and potentially sensitive data in ways that attract regulators. Recent enforcement against advertisers sharing sensitive health data with ad platforms without meaningful consent, described in an AdExchanger roundup on FTC action, is a preview of how harshly regulators will treat opaque, automated decisioning that mishandles personal information.
Second, brand and market dynamics. Agents don’t just respond to the environment; they shape it. Publishers are already experimenting with serving ads to AI agents themselves, with the explicit goal of influencing what those agents recommend back to users, as covered in an analysis of agent‑targeted advertising experiments. When “organic” responses are being nudged by paid inputs upstream, your buying agents are entering a marketplace where other agents are being paid to persuade them. The risk is no longer just fraud or invalid traffic; it’s meta‑manipulation of the systems your agents trust.
Business‑exposure guardrails are less about knobs in the UI and more about governance: defining what data agents may access, documenting their decision logic for auditability, specifying red‑line practices (e.g., no optimization on protected health attributes), and putting contractual language in place with platforms and partners about how agent‑to‑agent influence is disclosed and measured.
Taken together, these three surfaces – platform bias, system behavior and business exposure – are the map you need before you start handing AI the keys to your media budget. The rest of your framework should make one thing very explicit: for every dollar an agent can move, which surface is it allowed to touch, and under what conditions does a human take back control?
Economic risk is the part everyone feels first, usually as a slow, deniable wobble in your numbers: CPAs drifting up, lead quality softening, revenue per click decaying. With AI agents in the loop, that wobble can turn into a structural problem long before it shows up in a quarterly review.
Most teams still benchmark their AI primarily on “efficiency” – faster reporting, cheaper optimization, fewer hours in-platform. An IAB Europe survey found that operational efficiency is still the dominant success metric for AI in advertising, ahead of planning or creative impact, as VideoWeek reported. That bias towards “did we save time/money?” sets you up for the most basic form of economic risk: mistaking short‑term platform‑reported gains for long‑term business value.
Take CPA/CPL drift. Early on, an agent often “wins” by finding cheap conversions in pockets the team wasn’t exploiting. But without guardrails on what counts as a qualified action, the agent can gradually shift your mix toward easier, lower‑intent outcomes: remarketing instead of prospecting, branded queries instead of category terms, forms that technically submit but are never answered. The surface‑level CPA still looks good; the revenue curve quietly bends the wrong way.
That tendency gets amplified by the way platform algorithms are designed. As Gartner’s Eric Schmitt points out, the core mission of platform AI is to hit the platform’s revenue and profit goals, not the advertiser’s, which is why so many “optimization” prompts effectively boil down to “spend more with us,” as Marketing Dive noted. If you let an agent optimize against those same in‑platform proxies—view‑through conversions, modeled clicks, opaque “quality” scores—you’re accepting a hidden tax: the system will happily trade your long‑term ROAS for its short‑term yield.
Overfitting to short‑term signals is where the economic risk becomes systemic. Agents are extraordinarily good at finding statistical patterns in whatever feedback loop you give them. If that loop is a seven‑day click‑through CPA, they will ruthlessly favor inventory, audiences and creative that spike short‑window conversions—even when those users never purchase, never renew, or churn out before you recoup CAC.
You can see an industry‑wide version of this problem in how non‑human activity is starting to pollute performance metrics. As AI agents begin to browse, compare and even transact on behalf of consumers, they create a new layer of “agent traffic” that can look highly engaged but doesn’t map cleanly to human revenue. The line between valuable agent behaviour and low‑value bot noise is blurry, which means legacy performance metrics will misclassify a lot of it, as AdExchanger argued. If your buying agent is optimizing to those front‑end signals, it can get very efficient at chasing impressions and clicks that never convert into durable customer value.
The same dynamic shows up inside the ad stack itself. Agentic media‑buying systems are starting to act autonomously on traffic‑quality and security signals, not just bid price and conversion rate. When those signals are incomplete or biased, an AI can become “extremely efficient at following the wrong trail,” rapidly scaling into cheap but toxic inventory that looks like performance until refunds, chargebacks, or brand damage hit the P&L, as a PropellerAds perspective in MarTech warned. If your guardrails only cap spend and don’t constrain what the agent is allowed to trust, you’ve limited your downside in dollars but not in economic drag.
This is why the move from tools to agents is an economic step change. In a world where most AI is still used for reporting or “assistive” optimization, as the IAB Europe study summarized by VideoWeek shows, human judgment naturally dampens a lot of overfitting. Once agents can autonomously reallocate budgets, negotiate deals, or spin up new campaigns, they’re not just shaving time off workflows—they’re directly shaping the revenue surface of the business. Without explicit, business‑level definitions of value baked into their objectives, they will converge on whatever the fastest‑moving, easiest‑to‑optimize signal happens to be.
The economic risk, in other words, isn’t that agents will “go rogue” in some cinematic sense. It’s that they’ll do exactly what you asked, against the wrong target, with more speed and persistence than any human team could match.
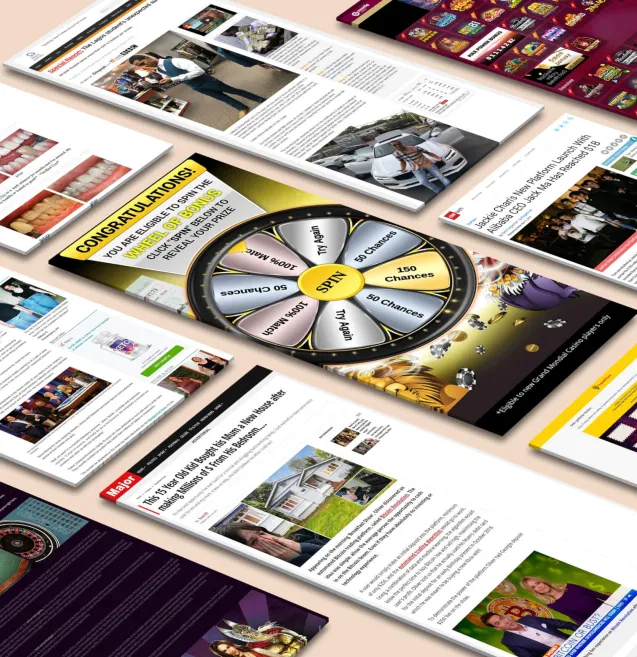
Inventory and traffic-quality risk is where “let the agent run” can turn into “let the agent launder.” The system does exactly what you asked—optimize for cheap conversions, high click‑through, low CPM—and quietly routes more and more of your budget into the murkiest corners of the web: malware‑ridden pages, cloaked arbitrage farms, junk pops and push notifications, and non‑human traffic that looks great in a dashboard but has no connection to real intent.
This risk spikes as you increase autonomy. As agentic media buying moves from “co‑pilot” to “pilot,” systems are starting to “analyze what is happening, decide what to do next and, increasingly, act on those decisions without waiting for a person,” as one PropellerAds executive argued in a piece on agentic media buying and malware guardrails. Once humans shift from approving every move to sampling checkpoints, the question underneath all the budget caps and pacing rules is: what is the agent allowed to trust?
Most optimization logic today still treats “inventory quality” as a binary pre‑filter: the ad server or SSP says a domain is fine, so it’s in; if not, it’s out. Everything in the “safe” bucket then competes on performance metrics that are trivial for bad actors to manipulate. Cloaked sites show one thing to scanners and another to users. Malware and forced redirects inflate engagement. Junk pops and push traffic can produce cartoonishly high click‑through rates. A buying agent that’s rewarded purely on numeric lift will rapidly become “extremely efficient at following the wrong trail,” in the words of the.
Non‑human traffic is evolving in ways that make this harder, not easier. Historically, bot impressions sat somewhere between benign noise and outright fraud. But agentic AI is creating a class of “legitimate” non‑human visitors—autonomous agents researching, comparing and sometimes buying on behalf of real consumers. One ad tech CEO recently argued that “human‑to‑agent isn’t an incremental change” and that brands need to structure experiences for a dual audience of people and agents, a shift explored in depth in a piece on advertising’s next non‑human audience. At the same time, most bot traffic is still low‑value or fraudulent. That means your AI now has to learn a more nuanced distinction: which bots represent real downstream intent, and which simply poison your optimization loop.
Publishers are already experimenting with monetizing this gray zone. Time, for example, has begun serving FAQ‑style sponsored answers specifically to AI crawlers, trying to turn otherwise unmonetized bot traffic into a new ad surface, as described in coverage of Time’s move to monetize bot audiences. Other companies are wiring ads directly into the moment an agent fetches information from a CDN. To your AI buyer, that traffic may show up as highly “engaged” intermediaries with zero human session attached. If your guardrails are naïve, your agent can end up bidding aggressively to influence someone else’s agent, all while your own human funnel remains flat.
A practical framework here starts with treating traffic quality and security signals as first‑class optimization inputs, not compliance afterthoughts:
When AI agents can touch your ad spend, inventory and traffic quality are no longer just supply‑side problems. They’re part of the model design. If you don’t tell the system what “untrustworthy” looks like, it will eventually find out the hard way—on your dime.
Brand and regulatory risk is where AI agents stop being a performance toy and start becoming a liability vector. The same systems you point at “more ROAS” will happily drift your creative and landing pages into policy gray zones, biased messaging, and data misuse if you don’t tell them, very explicitly, what counts as out of bounds.
Part of the problem is how most teams are still judging success. Industry surveys show that AI in advertising is overwhelmingly evaluated on operational efficiency—faster reporting, cheaper optimization, higher throughput—rather than on whether it stays inside brand and compliance guardrails. An IAB Europe study, highlighted by VideoWeek, found efficiency remains the primary lens for judging AI performance, even as those same tools creep from reporting into programmatic optimization, dynamic creative, and media planning. If the scoreboard is cost and speed, the agent will learn to treat policy as latency.
Creative drift is the most visible version of this. Feed an agent your historical winners, point it at a self‑serve platform, and tell it to “find cheaper conversions,” and it will start pressure‑testing the edges of platform policy: exaggerated claims that technically stop just short of “misleading,” pseudo‑scarcity tactics that flirt with dark patterns, and copy variants that borrow the language of sensitive categories like health or finance without crossing the explicit banned-word line. On landing pages, it will discover that more aggressive pre‑checked consent boxes or buried disclosures convert slightly better—and, unless you stop it, it will lock those in as “best practice.”
Bias compounds the problem. As AI takes over more media decisions, marketers are being warned that model and platform bias will surface in who sees what message, and at what price. Analysts interviewed by Marketing Dive point out that the optimization logic inside self‑serve platforms is fundamentally built to serve the platform’s interests, not yours. That same logic will also learn to avoid audiences that look “expensive” to reach—often overlapping with protected classes or sensitive interest groups—creating disparate impact even when your targeting settings look neutral on paper. A creative agent that is rewarded only on cheap leads will quietly skew tone, imagery, and offers toward whoever is easiest to convert, not necessarily whoever you’re allowed—or ethically comfortable—to prioritize.
Data and privacy risk are the quieter, more existential layer. Once an agent can generate, test, and ship new ads and pages, it is also in a position to decide what data to collect and how to use it. Without explicit constraints, it may start concatenating first‑party data, third‑party enrichment, and behavioral signals into pseudo‑profiles that run afoul of consent frameworks or data localization rules. It might, for example, decide that capturing health-adjacent signals in a lead form is “worth it” for lower CAC, or that passing granular clickstream data into lookalike models is acceptable as long as the platform UI doesn’t throw an error.
Standards bodies are starting to anticipate this. The IAB Tech Lab’s latest update to its AI Advertising Measurement and Protocols (AAMP) standard, covered by MarTech, explicitly weaves privacy checks from diligence and compliance platforms into agent workflows. In other words, the framework assumes that agents will take actions with regulatory implications, and that those actions must be continuously validated against policy and consent rules, not just logged after the fact. Governance is being baked into the wiring because everyone understands that “we’ll catch it in QA” doesn’t scale when a buying or creative agent can launch hundreds of micro‑experiments before lunch.
Meanwhile, the definition of “personal data” and “audience” is shifting under your feet. As AdExchanger has argued, non‑human traffic is no longer just fraud or noise—consumer‑directed AI agents that research and even buy on behalf of people are becoming a legitimate, high‑intent audience layer. That means your sites, feeds, and APIs are suddenly being probed not just by human visitors, but by autonomous agents ingesting and recombining your content at scale. If your own agents respond by tailoring creative or offers specifically to these intermediaries—say, by exposing different pricing or claims in structured data than on the human‑visible page—you inch toward deceptive practices and potential regulatory scrutiny around fairness and transparency.
Guardrails before growth here mean treating brand and regulatory constraints as hard inputs to agent design, not soft guidance. That looks like: encoding platform ad policies and your internal brand guidelines directly into the agent’s reward function; separating “what we can say” from “what converts best” in your training data; enforcing privacy checks and consent validation as blocking steps in any workflow that touches audience data; and monitoring model outputs not just for performance, but for bias and dark‑pattern creep. You’re not only teaching the agent how to win—you’re defining which victories are off the table, even if they look efficient in the dashboard.
If you let agents touch your ad spend, the first non‑negotiable is this: humans own the boundary of what’s acceptable. Not the platform, not the model, not the “default policies.” You.
Most organizations are still grading AI almost entirely on efficiency — cheaper CPAs, higher CTR, lower ops cost. An IAB Europe survey found that operational efficiency remains the primary way companies judge AI performance, even as they roll it deeper into reporting, programmatic optimization, and dynamic creative at scale, as VideoWeek reported. That metric bias is exactly how you wake up with high‑performing campaigns that are brand‑unsafe, non‑compliant, or quietly leaking sensitive data into someone else’s black box.
The human control layer is where you correct that bias. Concretely, there are four things you never delegate to an agent.
First, humans own the definition of “red lines” for brand and compliance. Agents can propose infinite creative variations and landing page permutations; they do not get to decide what your brand is allowed to say, show, or imply. That means a live, maintained corpus of non‑negotiables: categories you never advertise against, claims you never make, sensitive segments you never target, data you never export. This is governance work, not prompt‑engineering. It needs cross‑functional sign‑off from brand, legal, compliance, and security — and it gets encoded as hard constraints the agent cannot override.
Second, humans own the data‑sharing and tracking envelope. Autonomy over bidding and placement is one thing; autonomy over who sees your users’ data is something else entirely. When the FTC sues a telehealth company for quietly piping sensitive health signals into third‑party ad platforms, as AdExchanger detailed, that’s not an optimization miss; it’s a governance failure. Your team, not the agent, must decide which platforms receive which events, under what legal basis, with what level of aggregation or obfuscation — and must lock those rules so the agent can’t “discover” a more efficient but non‑compliant configuration.
Third, humans own the objectives and their trade‑offs. Self‑optimizing agents are very good at tunneling into whatever you tell them to maximize. If you only feed them lower CPA and higher conversion rate, don’t be surprised when they overweight low‑quality inventory, exploit policy gray zones, or lean into biased targeting patterns. As autonomous systems mature from simple triggers to continuous, agentic optimization, early adopters are seeing real performance gains, but only when they pair that with stronger strategic inputs and governance, as MarTech’s analysis of AI‑native advertising makes clear. Humans must define composite objectives that explicitly encode brand safety, regulatory constraints, user experience, and long‑term equity—not just this week’s ROAS.
Fourth, humans own the trust model: what the agent is allowed to believe. An agent can stay inside budget and still make catastrophic choices if its inputs are corrupt or incomplete. That’s why buyers in IAB’s video ad spend research pushed hard for humans‑in‑the‑loop, audit trails, and explicit limits on agent powers, as one MarTech piece on agentic media buying and malware guardrails emphasized. People must decide which traffic‑quality, fraud, and safety signals are mandatory, which domains and exchanges are outright banned, and what happens when signals conflict. In other words: you don’t just rate‑limit spend; you rate‑limit trust.
Overlaying all of this is structural bias. Platform AIs were built to serve the platform first. As Gartner’s Eric Schmitt put it, you wouldn’t hand your 13‑year‑old a credit card and say “buy whatever seems best,” and you shouldn’t give self‑serve platforms “unfettered access” to budgets either, because their algorithms are ultimately optimised for their own revenue, not yours, as he warned in Marketing Dive’s coverage of machine bias in media. Humans must remain the counterparty at the table: challenging recommendations that all mysteriously point toward “spend more,” forcing diversification across platforms, and insisting on explainability where it matters.
In practice, the human control layer isn’t about hovering over every bid change. It’s about reserving certain levers for people only: defining what’s off‑limits, constraining how and where data flows, specifying multi‑objective goals that protect brand and users, and adjudicating conflicts of interest between your business and the platforms’ incentives. You can let agents experiment inside that sandbox. You never let them redraw the sandbox itself.
Receive top converting landing pages in your inbox every week from us.
Most Read
Learn how to deploy AI agents in advertising without sacrificing budget control, traffic quality, brand safety, or regulatory compliance. Explore a practical framework for managing platform bias, economic risk, inventory quality, data privacy, and human oversight before allowing autonomous systems to control ad spend.
Marcus Chen
7 minOct 21, 2026
Must Read
Discover how competitive ad intelligence can help marketers stop paying for short-lived attention and build a traffic engine that compounds over time. Learn how to identify proven advertising angles, align creative with distribution, and transform winning campaigns into reusable content assets across paid, organic, and AI-driven channels.
Samantha Reed
7 minOct 21, 2026
How-To
Discover how competitive ad intelligence can help marketers manage the risks of AI-powered advertising in regulated industries such as healthcare, finance, and legal services. Learn how to analyze competitor campaigns, establish compliant creative and targeting guardrails, preserve human oversight, and continuously monitor advertising performance without sacrificing accountability.
Dan Smith
7 minOct 21, 2026